- oiste.org
- Root of Trust
- Policy Approval Authority
Root of Trust
Policy Approval Authority
The PAA administers the OISTE Global Trust Model. It determines whether every CPS and certificate policy is compliant and fit for purpose, and approves each change.
Mandate
A committee inside the foundation
The PAA has distinct functions but is not a separate legal entity. It develops, reviews and approves the practices, policies and procedures of the whole trust model, within guidelines set by the members and advisors of the foundation.
The PAA is composed of members selected by the Foundation based on their relevant knowledge and experience in PKI, certification authorities, compliance and sector-specific security requirements. In performing its functions, the PAA oversees the policies and practices governing the Trust Model, with due regard to the X.509 standard and other applicable international standards and industry requirements, with the objective of preserving the security, integrity and trustworthiness of the Root of Trust. Members may act as representatives of organisations or as independent experts contributing their expertise to the Trust Model.
Procedure
How a policy change is approved
- Step 1
Draft
A new version of the CPS or a CP is prepared.
- Step 2
Approve
Major changes need a PAA meeting and a memo signed by at least two members. Minor versions need one member.
- Step 3
Publish
The new version goes to the policy repository. The published version always prevails.
- Step 4
Assess
Each CA assesses the technical impact and changes its configuration where needed.
Members
PAA members
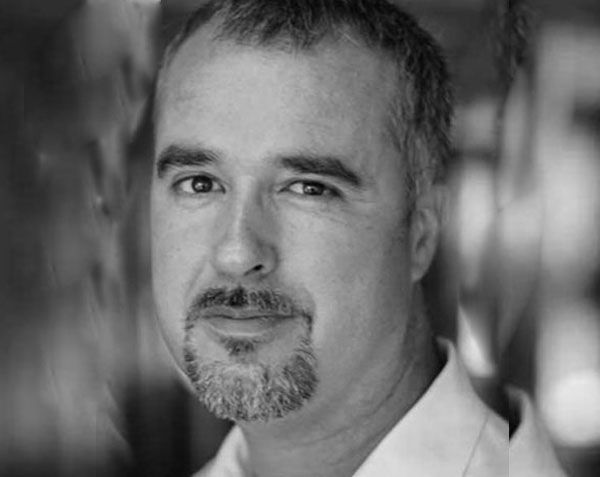
PAA member
Pedro Fuentes
Senior specialist in information security and PKI with more than 20 years of experience, responsible for PKI platforms and product strategy at WISeKey, which he joined in 2009. Previously led cybersecurity for southern Europe at Siemens. Computer Science, Polytechnic University of Valencia; CISM.
Contact
Write to the PAA
OISTE Foundation, OGTM Policy Approval Authority
29, route de Pré-Bois, CP 853, CH-1215 Geneva 15, Switzerland